What AI数据安全 Starts With
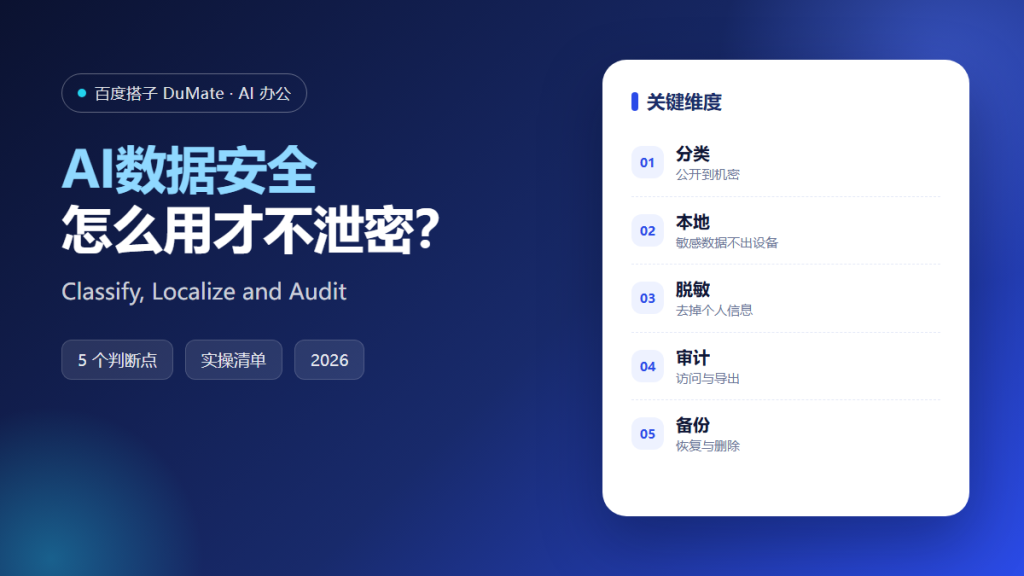
AI数据安全 starts with classification. If every file is treated the same, the team either blocks useful work or exposes sensitive material. A practical model separates public, internal, confidential, and restricted data before any tool sees it.
- Classify data before choosing a tool.
- Keep sensitive files on local or approved systems.
- Redact names, numbers, and account IDs.
- Log who accessed or exported a file.
- Define backup and deletion periods.
A Five-Step AI数据安全 Routine
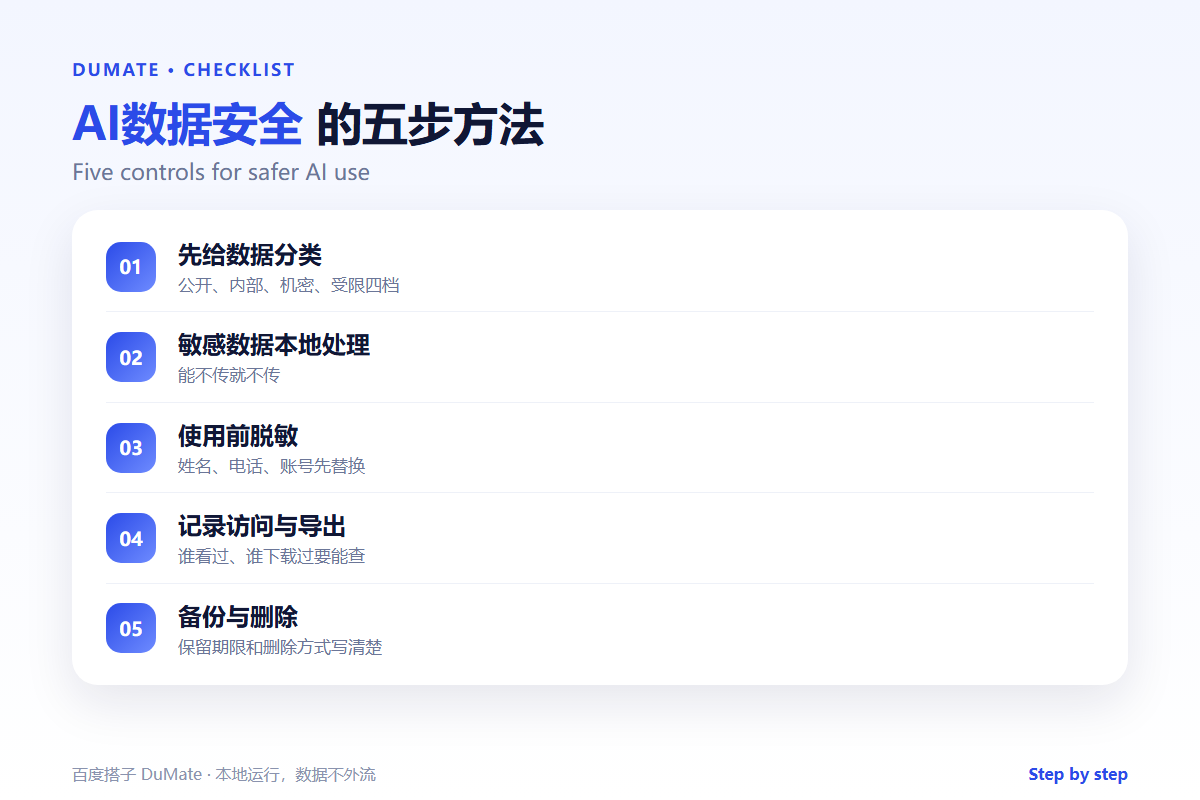
Start with one workflow and one data class. Test the controls on a small set. Then expand only after the access log and the deletion path are proven.
- Label the data class.
- Choose the processing location.
- Redact what is not needed.
- Record access and exports.
- Review retention and deletion.
Local is not automatically safe
A local tool can still leak through a misconfigured folder or an unlogged export. AI数据安全 is a combination of location, permission, and audit, not a single checkbox.
Where the Real Risks Sit
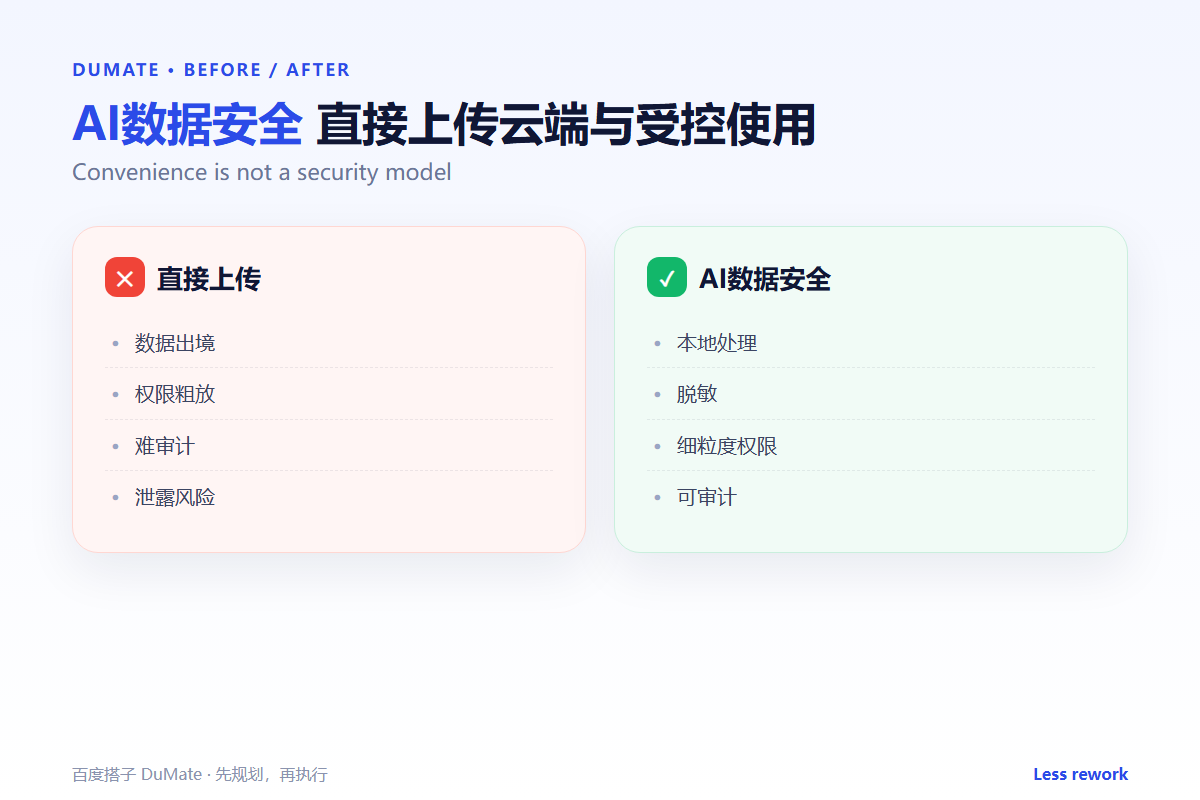
The risk is convenience: a quick upload to a cloud tool, a shared link that never expires, or a backup nobody remembers. Each one creates a path that the policy does not cover.
| Risk | Check | Fix |
|---|---|---|
| Cloud upload | Does the data class allow it? | Use local processing |
| Shared link | Does it expire? | Set an expiry date |
| Redaction | Are names and IDs removed? | Run a second check |
| Backup | Can it be restored and deleted? | Test both paths |
For the local-processing baseline, the 本地AI助手 guide explains what “stays on device” should mean. For enterprise controls, the AI私有化部署 checklist covers network and exit.
How to Evaluate AI数据安全
Ask for a data-flow diagram, a permission matrix, and a sample audit log. A good AI数据安全 answer will show where data is processed and how it is deleted. A poor one will answer with a slogan.
Start with one real task
Take a document with customer names. Run it through the approved workflow and check the output for identifiers. If any survive, the redaction step is not working.
What AI数据安全 cannot do
It cannot decide your legal obligations. It can support them with controls and evidence. The 企业AI助手 rollout guide covers the procurement conversation.
FAQ
Is local processing enough?
Only if permissions and logs are enforced. Local systems still need backups, patching, and access reviews.
What should we redact first?
Names, phone numbers, account IDs, and anything that identifies a person. Remove what the task does not need.
How long should logs be kept?
Long enough to investigate an incident and meet your policy. The AI权限管理 guide covers the review cycle.
References
评论
还没有评论,来说两句吧。以下为本文的引用通告: